The healthcare system has long been the target of cyberattacks — in recent years, hospitals and providers have disclosed attacks that led to operational disruptions and stolen data.
While medical device companies have not been exempt from the threat of cyberattacks, there were few incidents in the industry over the past several years. That changed this year, with a growing list of medtech firms hit by cyberattacks in recent months. The effects ranged from accessed and stolen data to operational disruptions that pressured earnings.
Stryker was one of the first medtech companies to disclose a cyberattack after its global Microsoft environment was targeted and disrupted. The attack shut down Stryker’s ordering, shipping and manufacturing capabilities for weeks and ate into its first-quarter results. The company said earlier this month that it is still recovering from the attack.
Days after Stryker’s attack, Intuitive said it was hit by a phishing incident that compromised employee and customer data.
And the attacks continued from there — Medtronic, Abbott, iRhythm, AdaptHealth, Cook Medical, Baylor Genetics and NovoCure were all hit by cyberattacks over the following months.
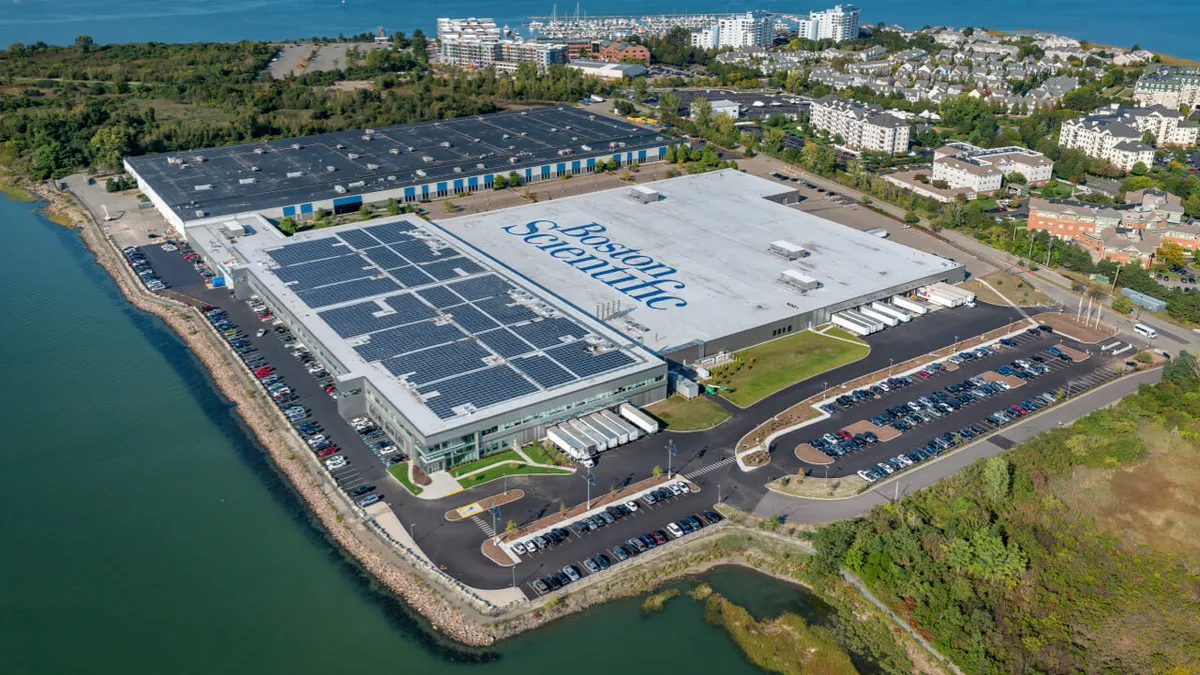
Boston Scientific is the most recent top medical device company to report a cyberattack. The company disclosed in late August that it identified an attack that targeted its internal systems, bringing down manufacturing, order processing and shipping. Operations were not fully restored until early September.
CEO Mike Mahoney said during a recent investor event that “all of our plants were shut down and distribution centers were shut down globally,” resulting in the company missing procedures due to hospital supply.
The company does not yet know how much of an impact the attack will have on its business, but it will provide more details next month on its earnings call.
Read on for MedTech Dive’s coverage of cyberattacks in the medical device industry: